

Log Explorer
Open Logs from the left navigation menu to access Log Explorer.
Log Explorer indexes logs from all connected services and applications. Use it to search large log volumes, inspect structured payloads, save frequently used queries, and investigate issues without leaving the platform.
Log Explorer Walkthrough
Section titled “Log Explorer Walkthrough”The main view combines a log volume graph with a result list. Each row in the list represents a single log entry and shows the most useful attributes for quick triage.
The graph shows log volume over time. The x-axis represents time and the y-axis represents the number of ingested log entries.
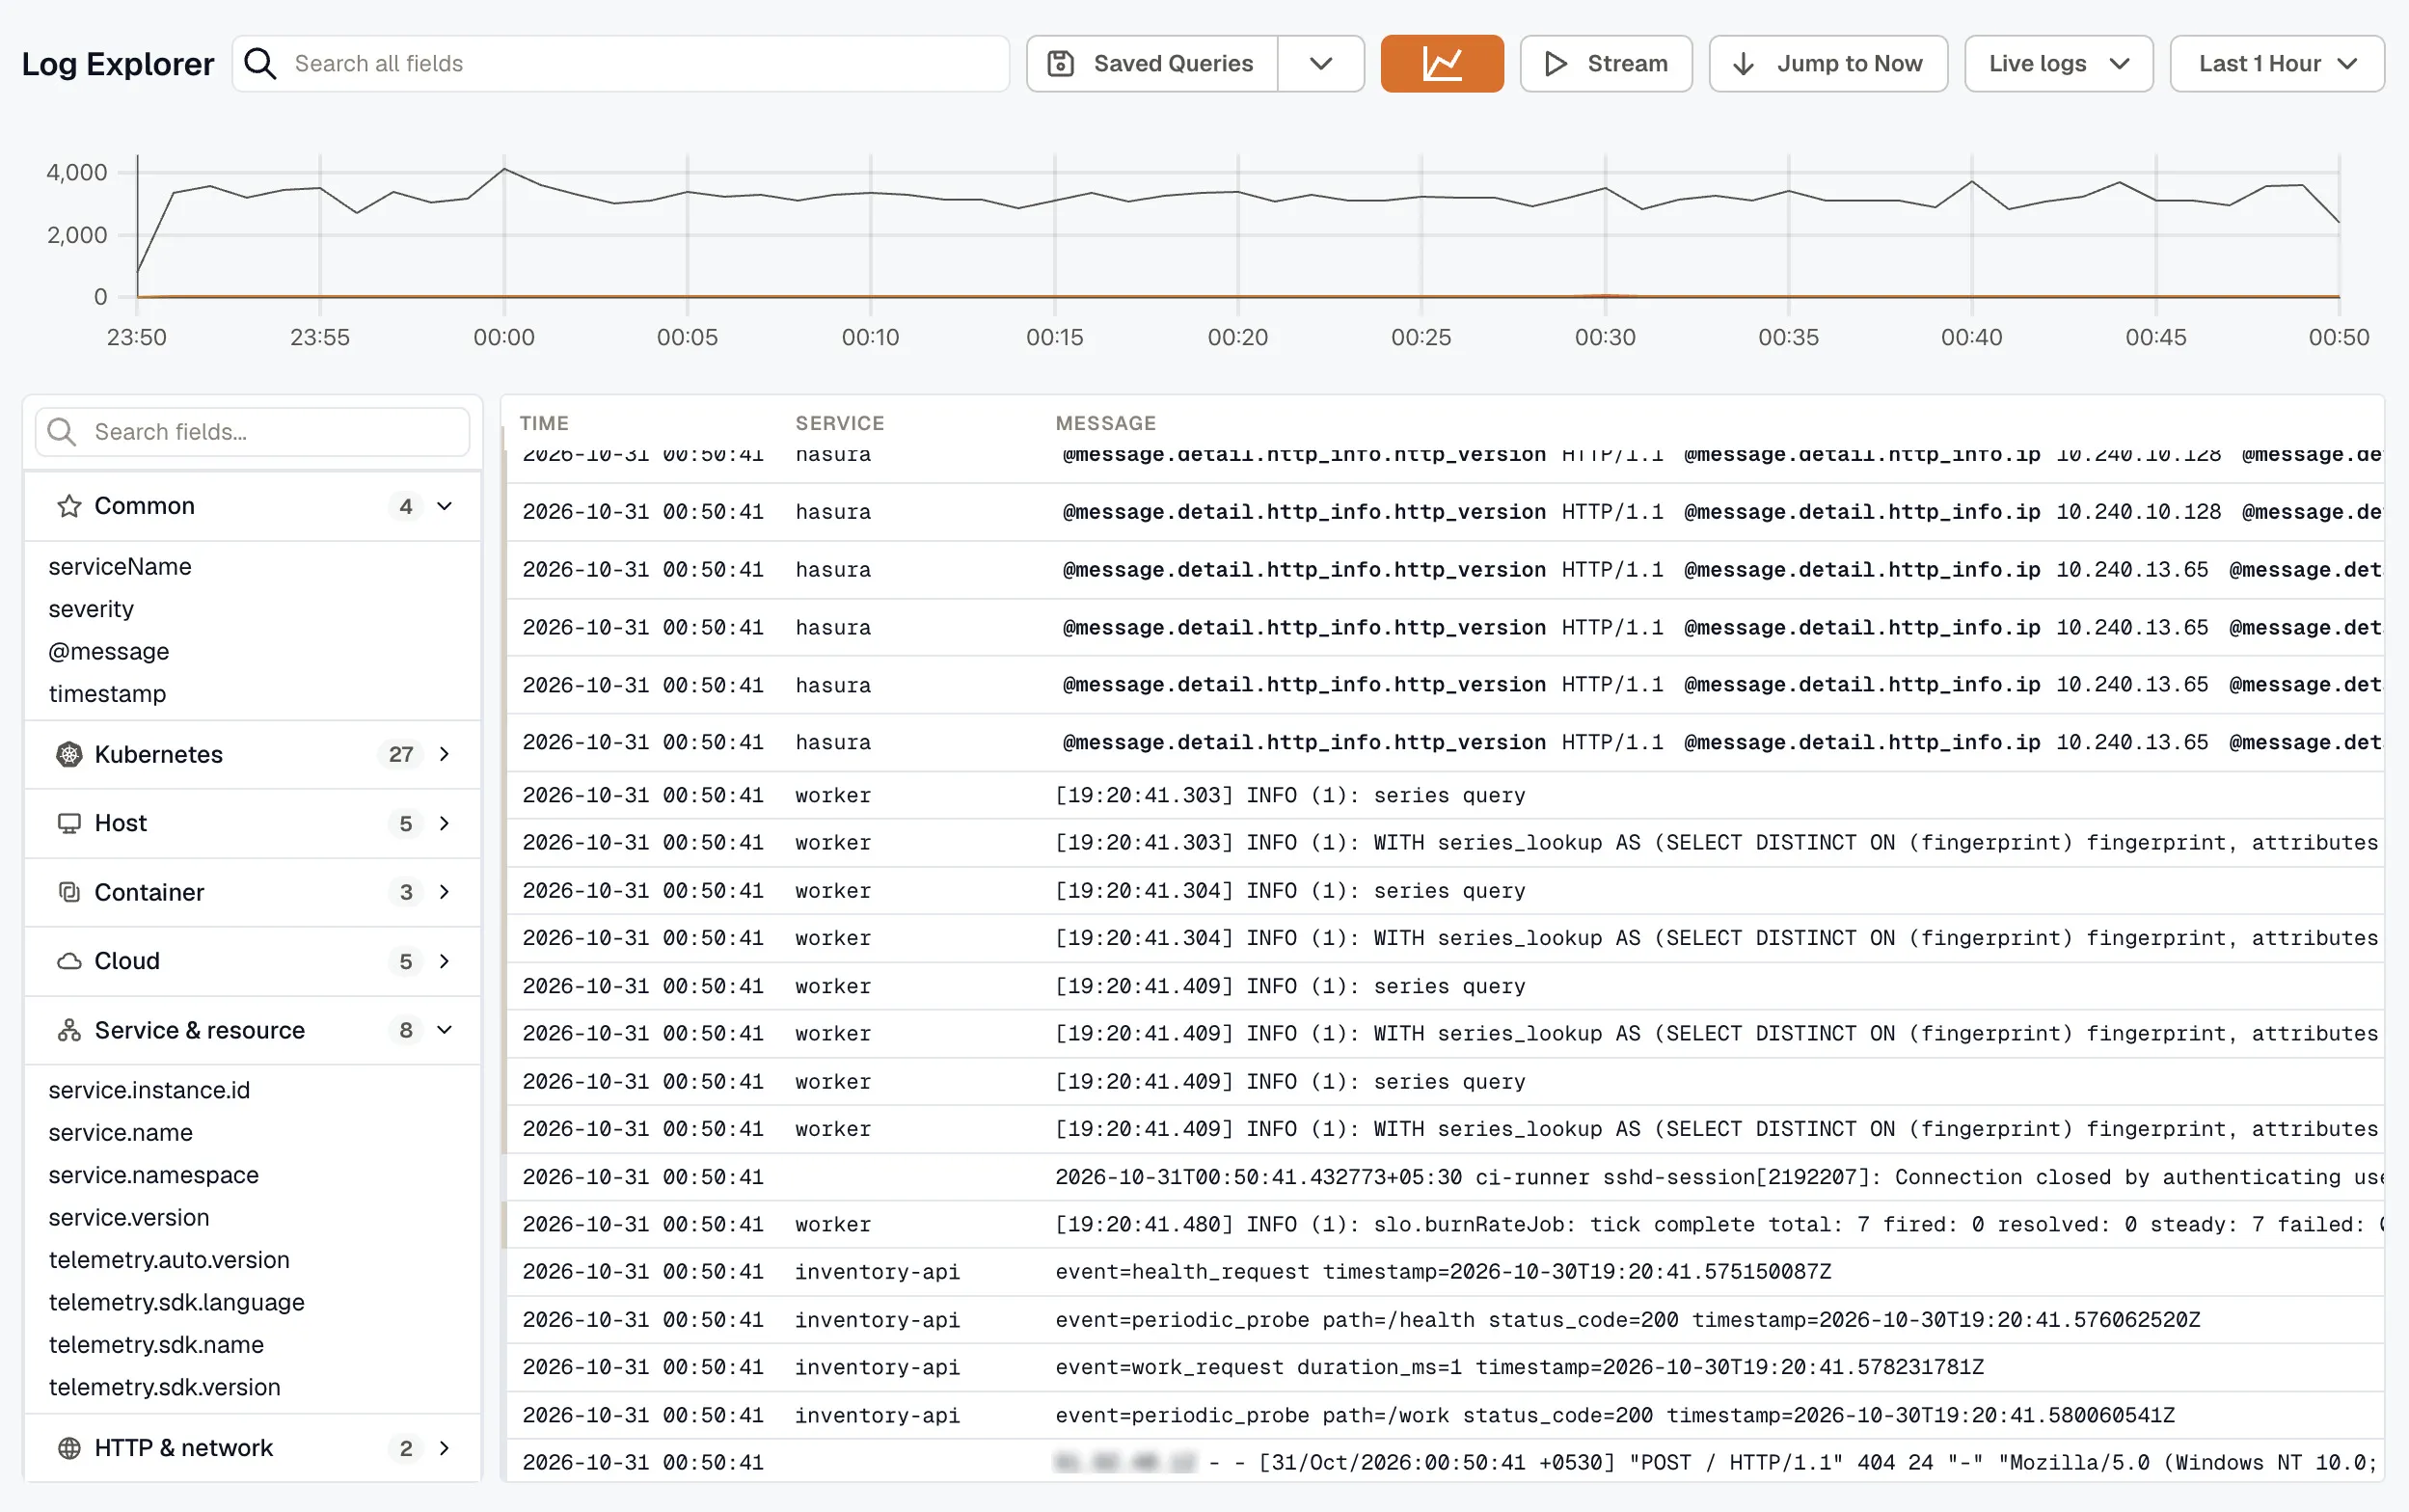
Select any log entry to inspect its full payload, labels, and metadata.
Search and Filter Logs
Section titled “Search and Filter Logs”Search
Section titled “Search”Use the search bar at the top of Log Explorer to find matching log entries across your environment.
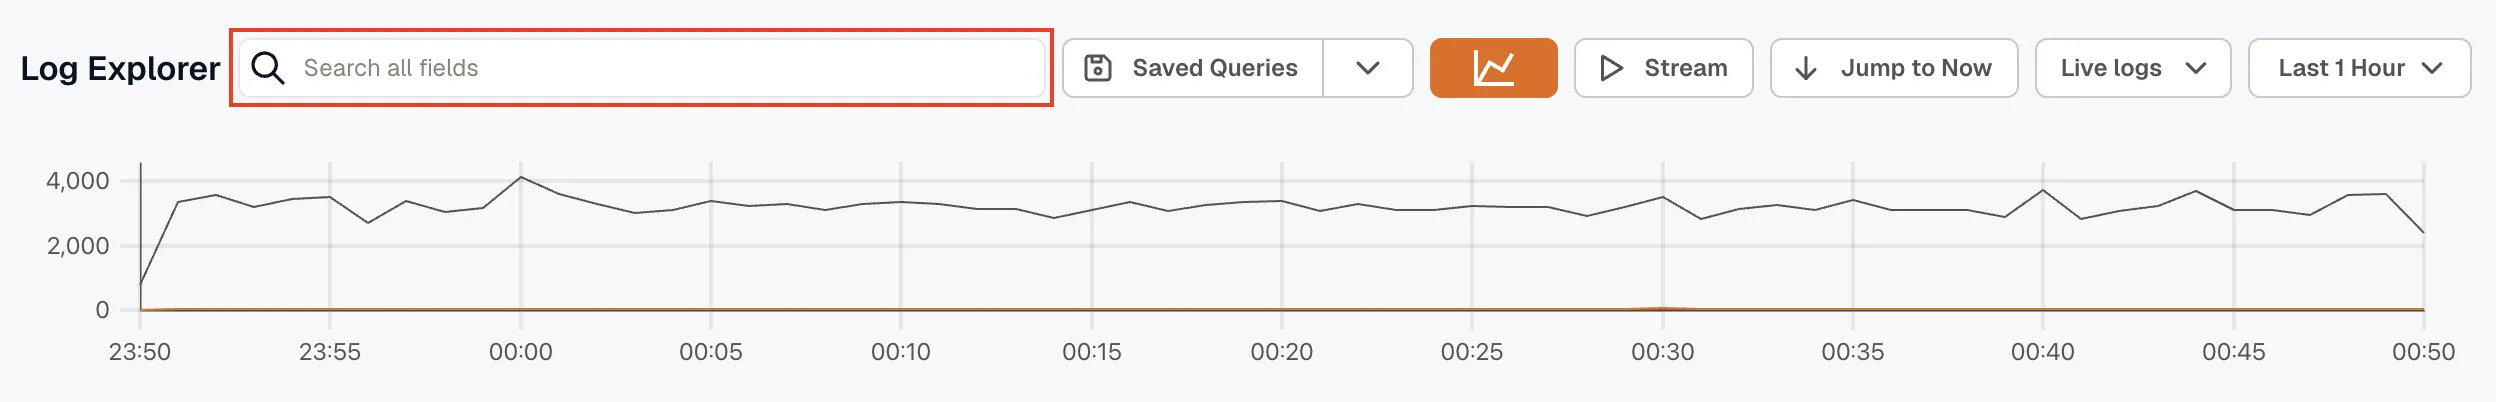
Refine results further by adjusting the selected time range from the time scale menu.
Filter
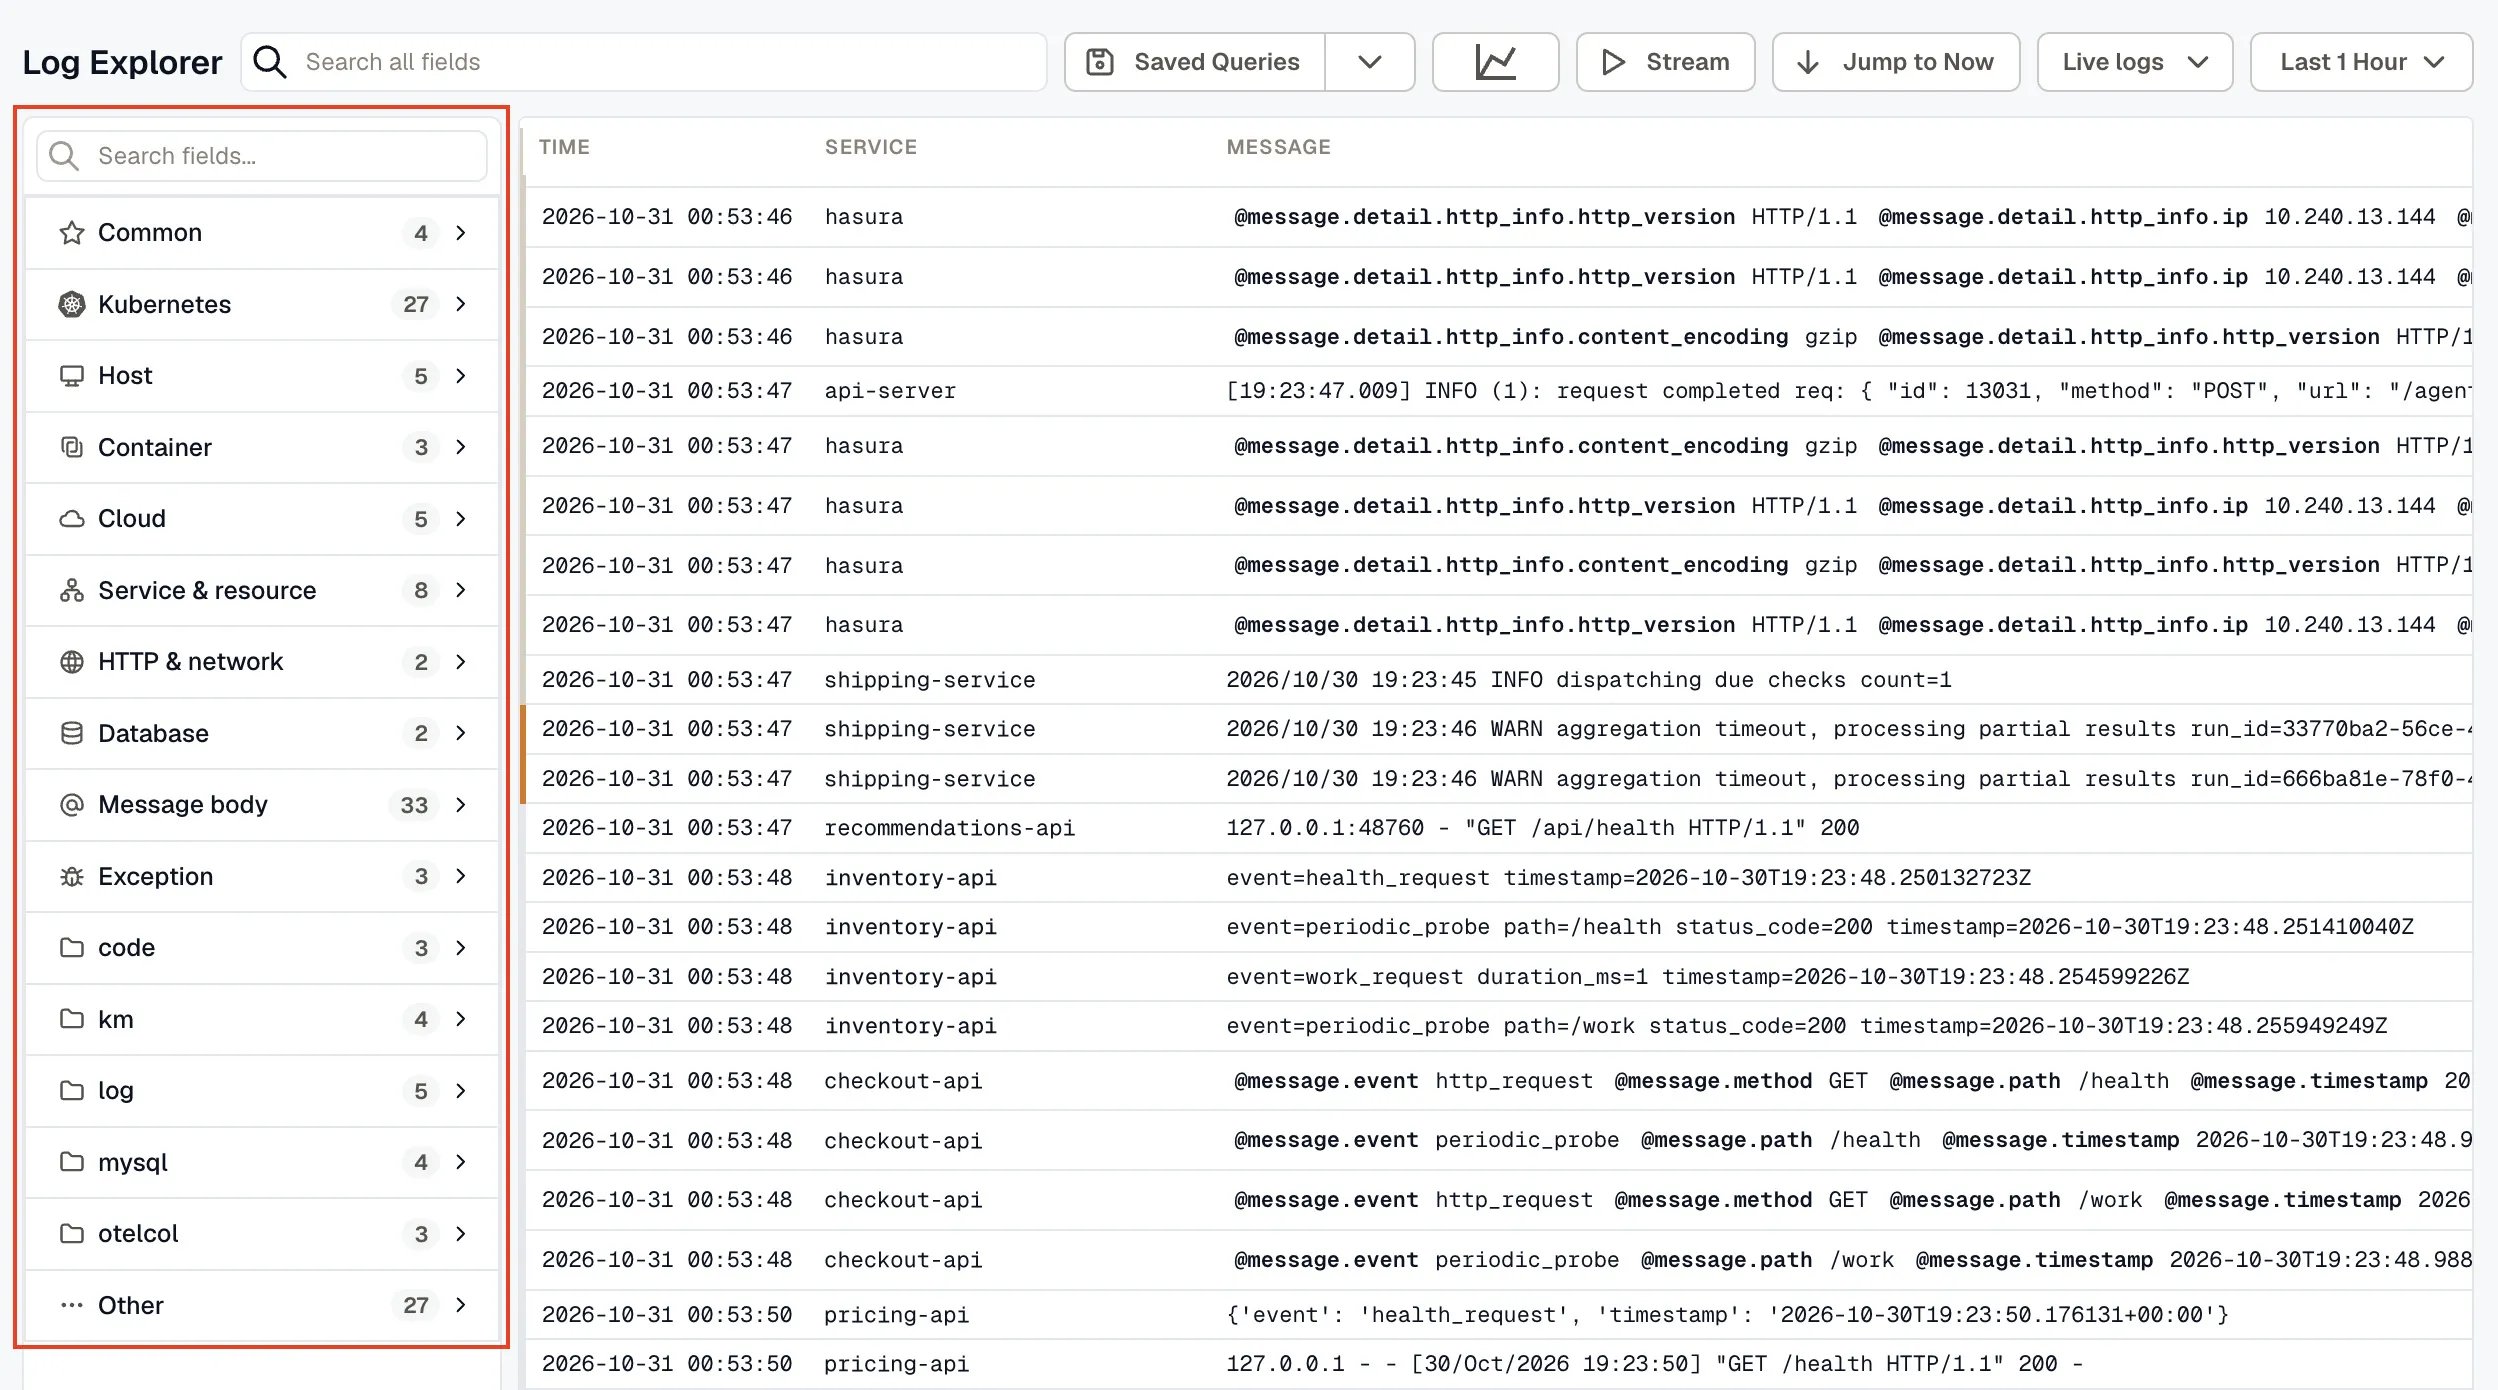
Section titled “Filter”Use the sidebar filters to narrow the result set by relevant dimensions. Combine multiple filters to isolate a specific set of logs.
Saved Queries
Section titled “Saved Queries”To save a query, click the dropdown arrow next to Saved Queries in the top-right area of Log Explorer. Enter a query name, description, and folder, then click Save.
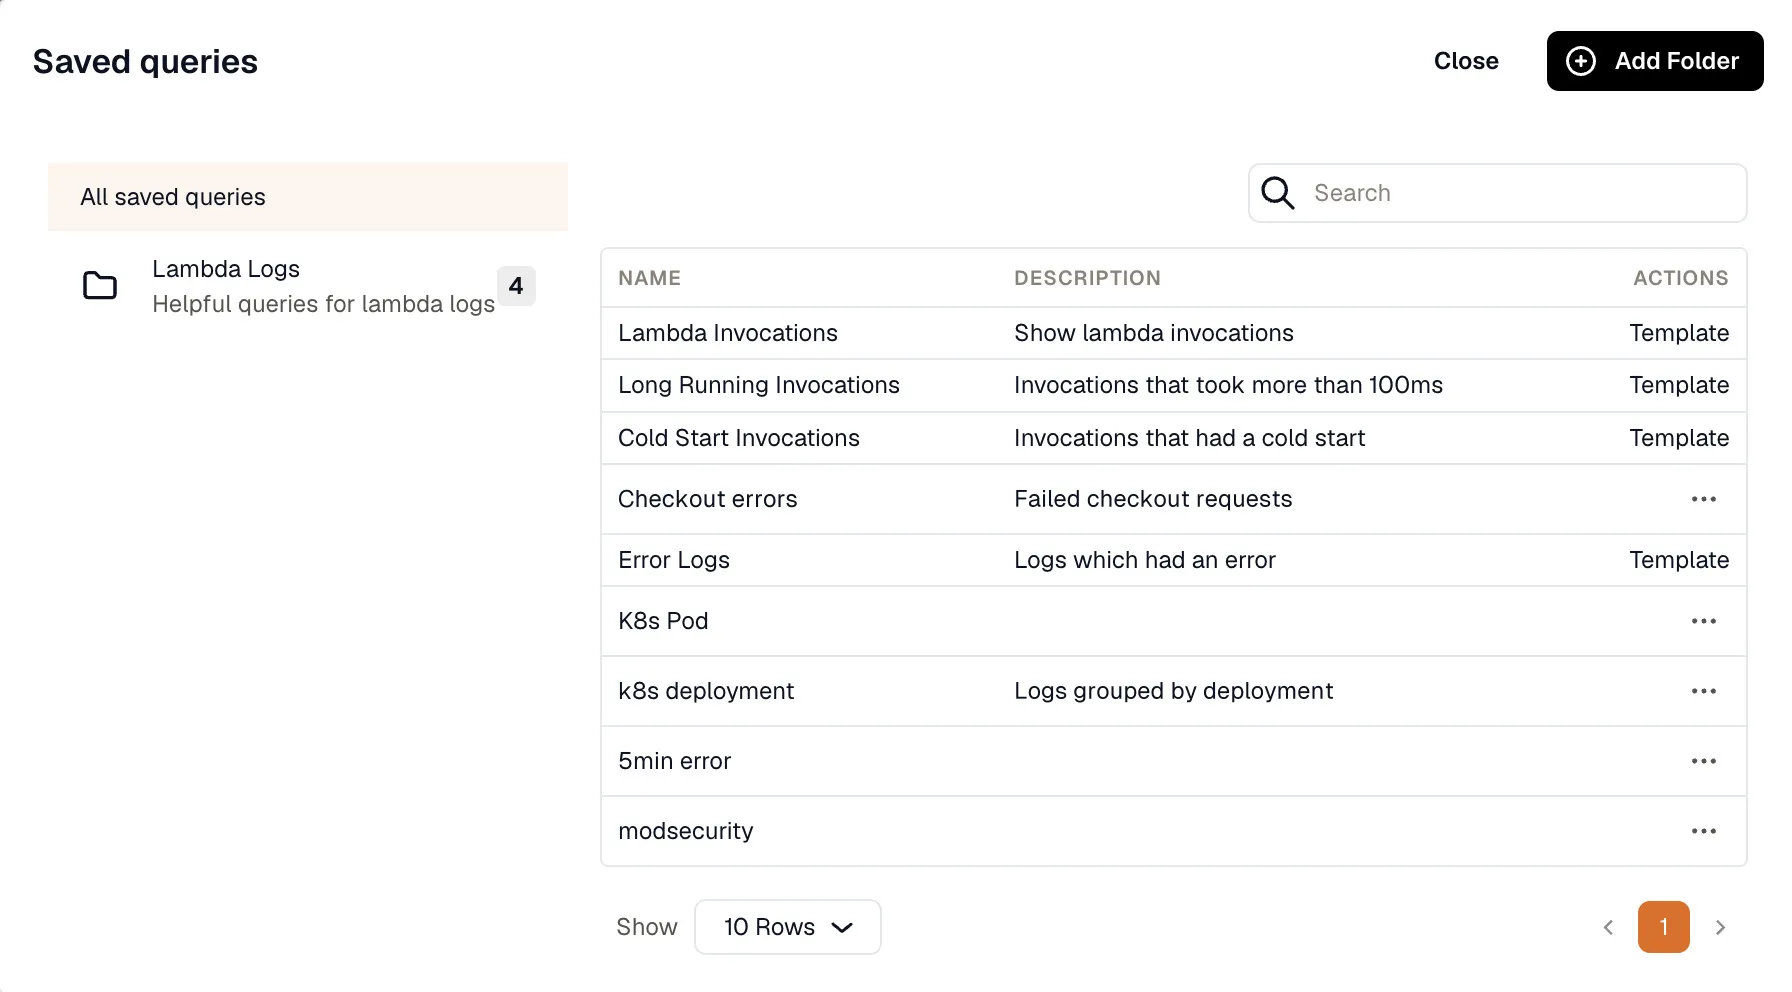
Saved queries remain available from the Saved Queries section for quick reuse.
Use folders to keep saved queries organized by service, team, or use case.
Inspect Log Entries
Section titled “Inspect Log Entries”Select any log entry to view detailed information and analysis.
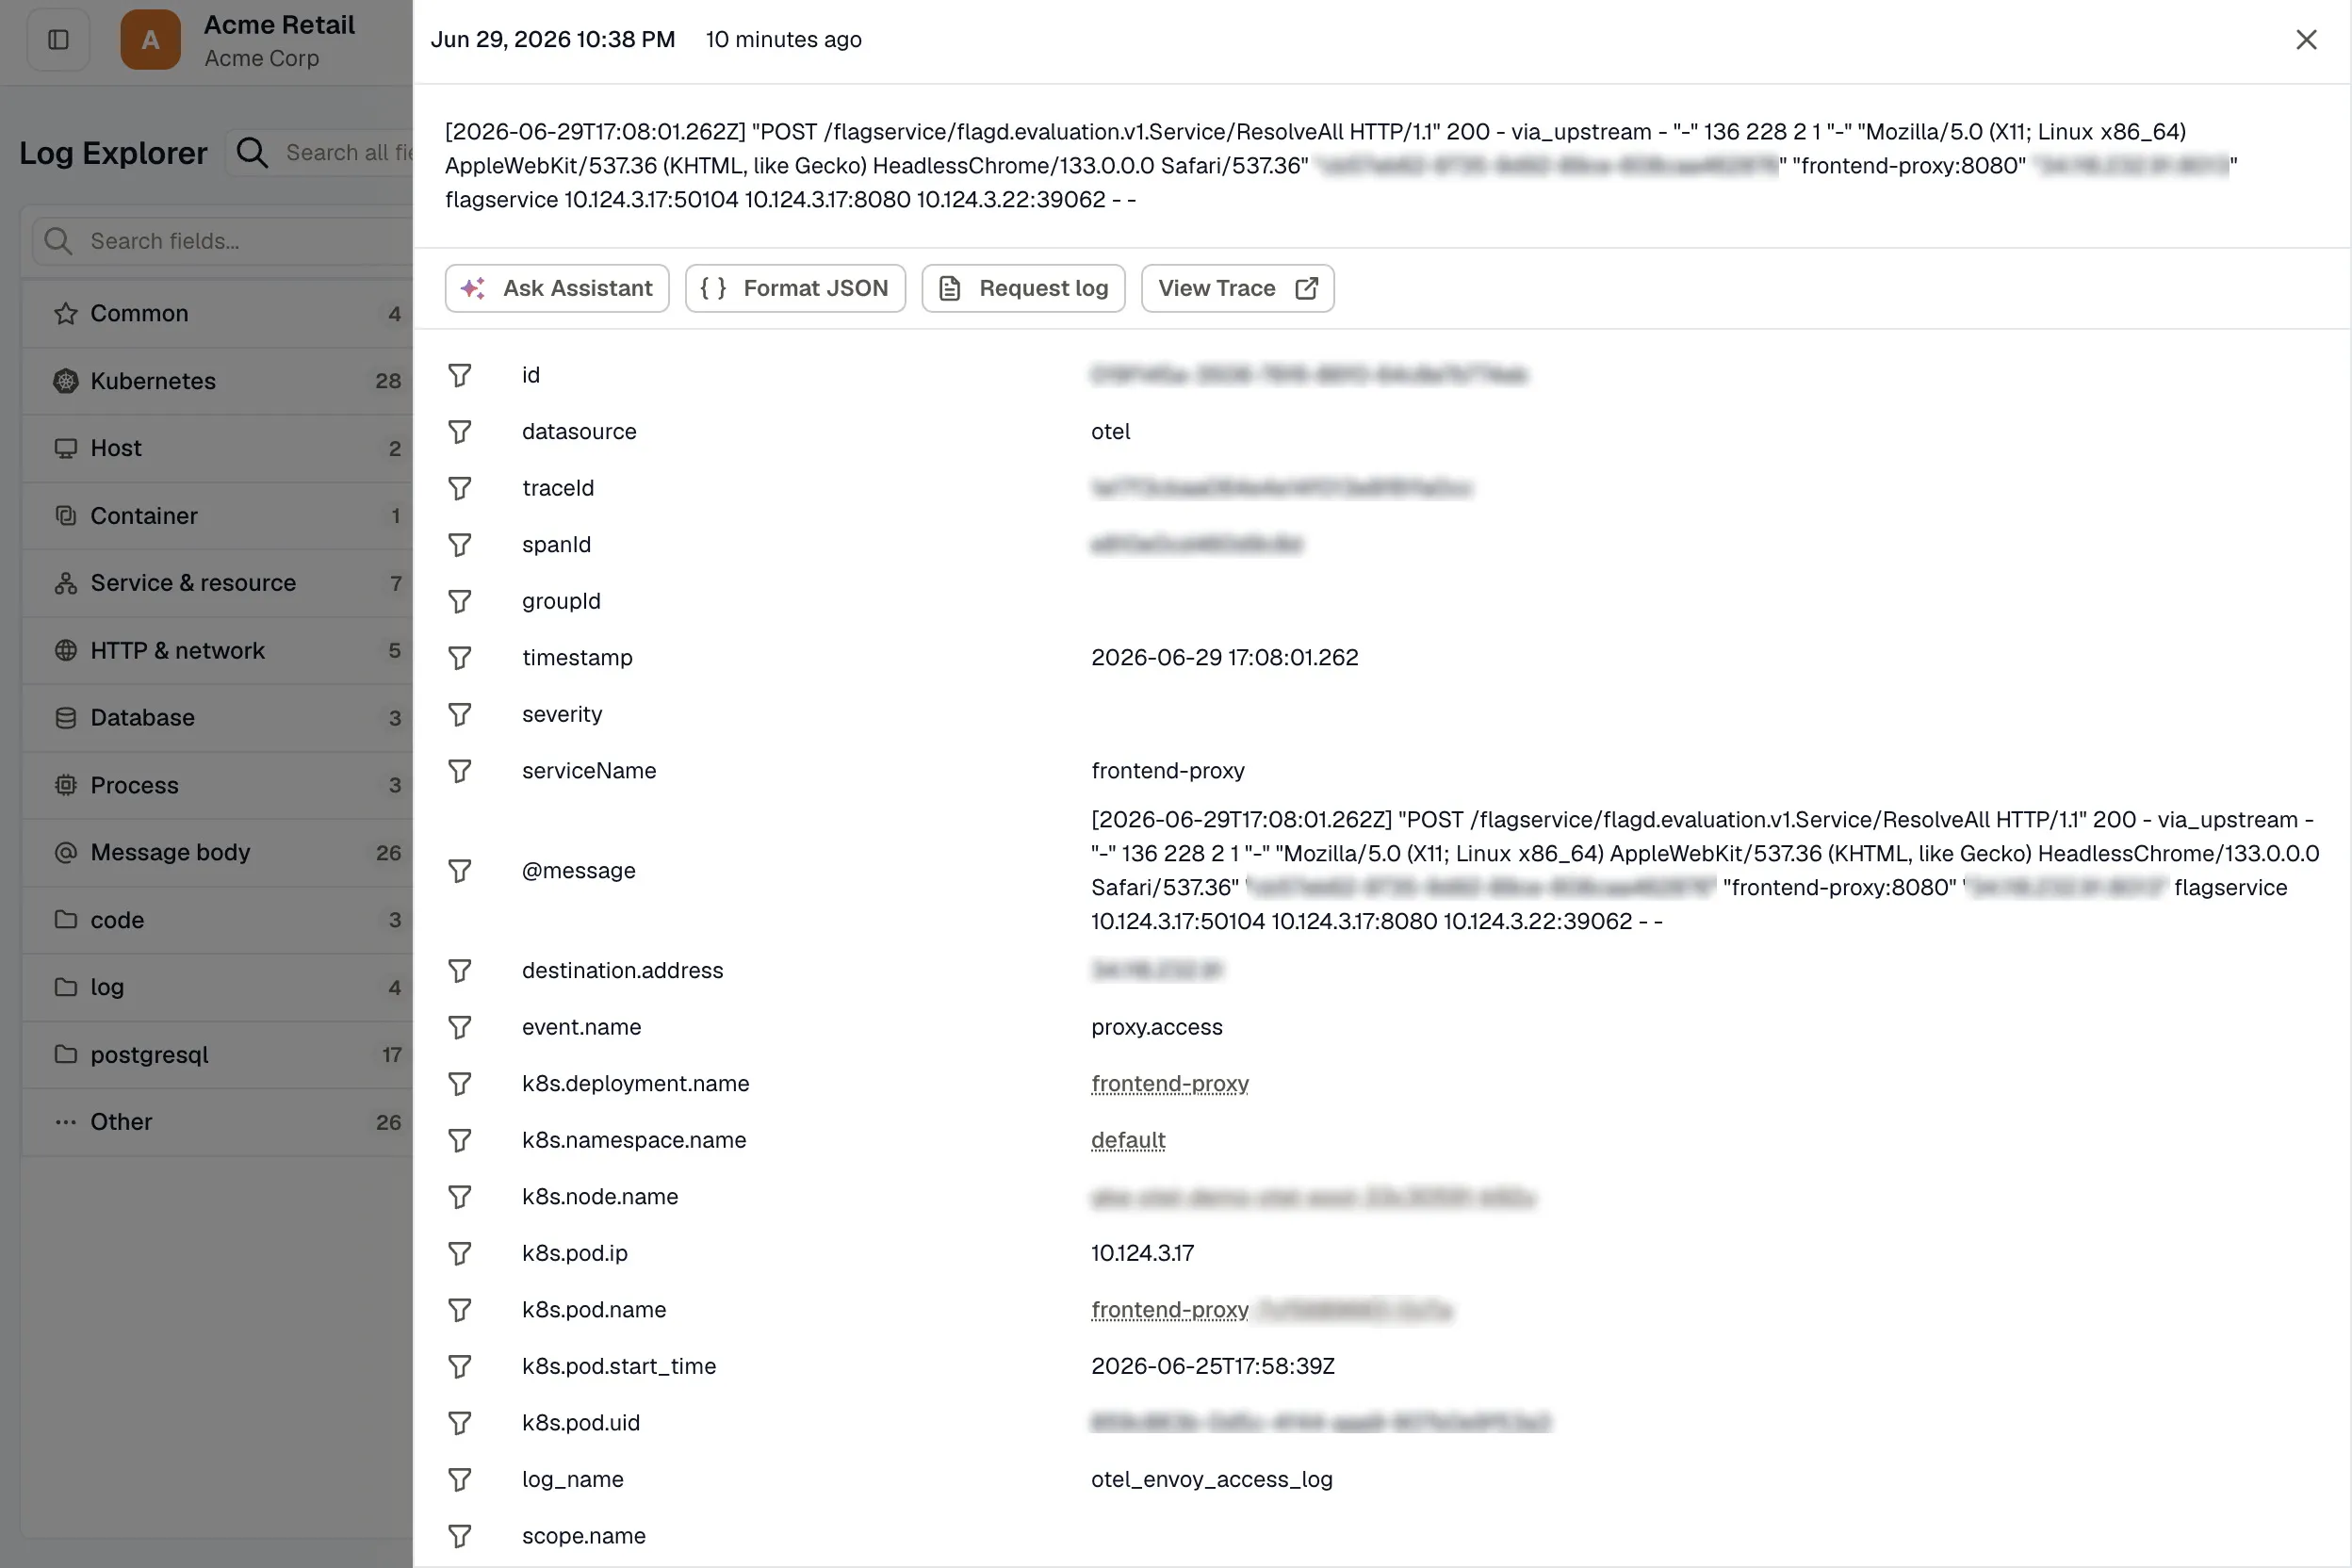
Ask Assistant opens KloudMate Assistant directly from the issue. It reviews the error log and its associated trace, generates a Log & Trace Summary, identifies the probable root cause, and suggests next steps for faster resolution.
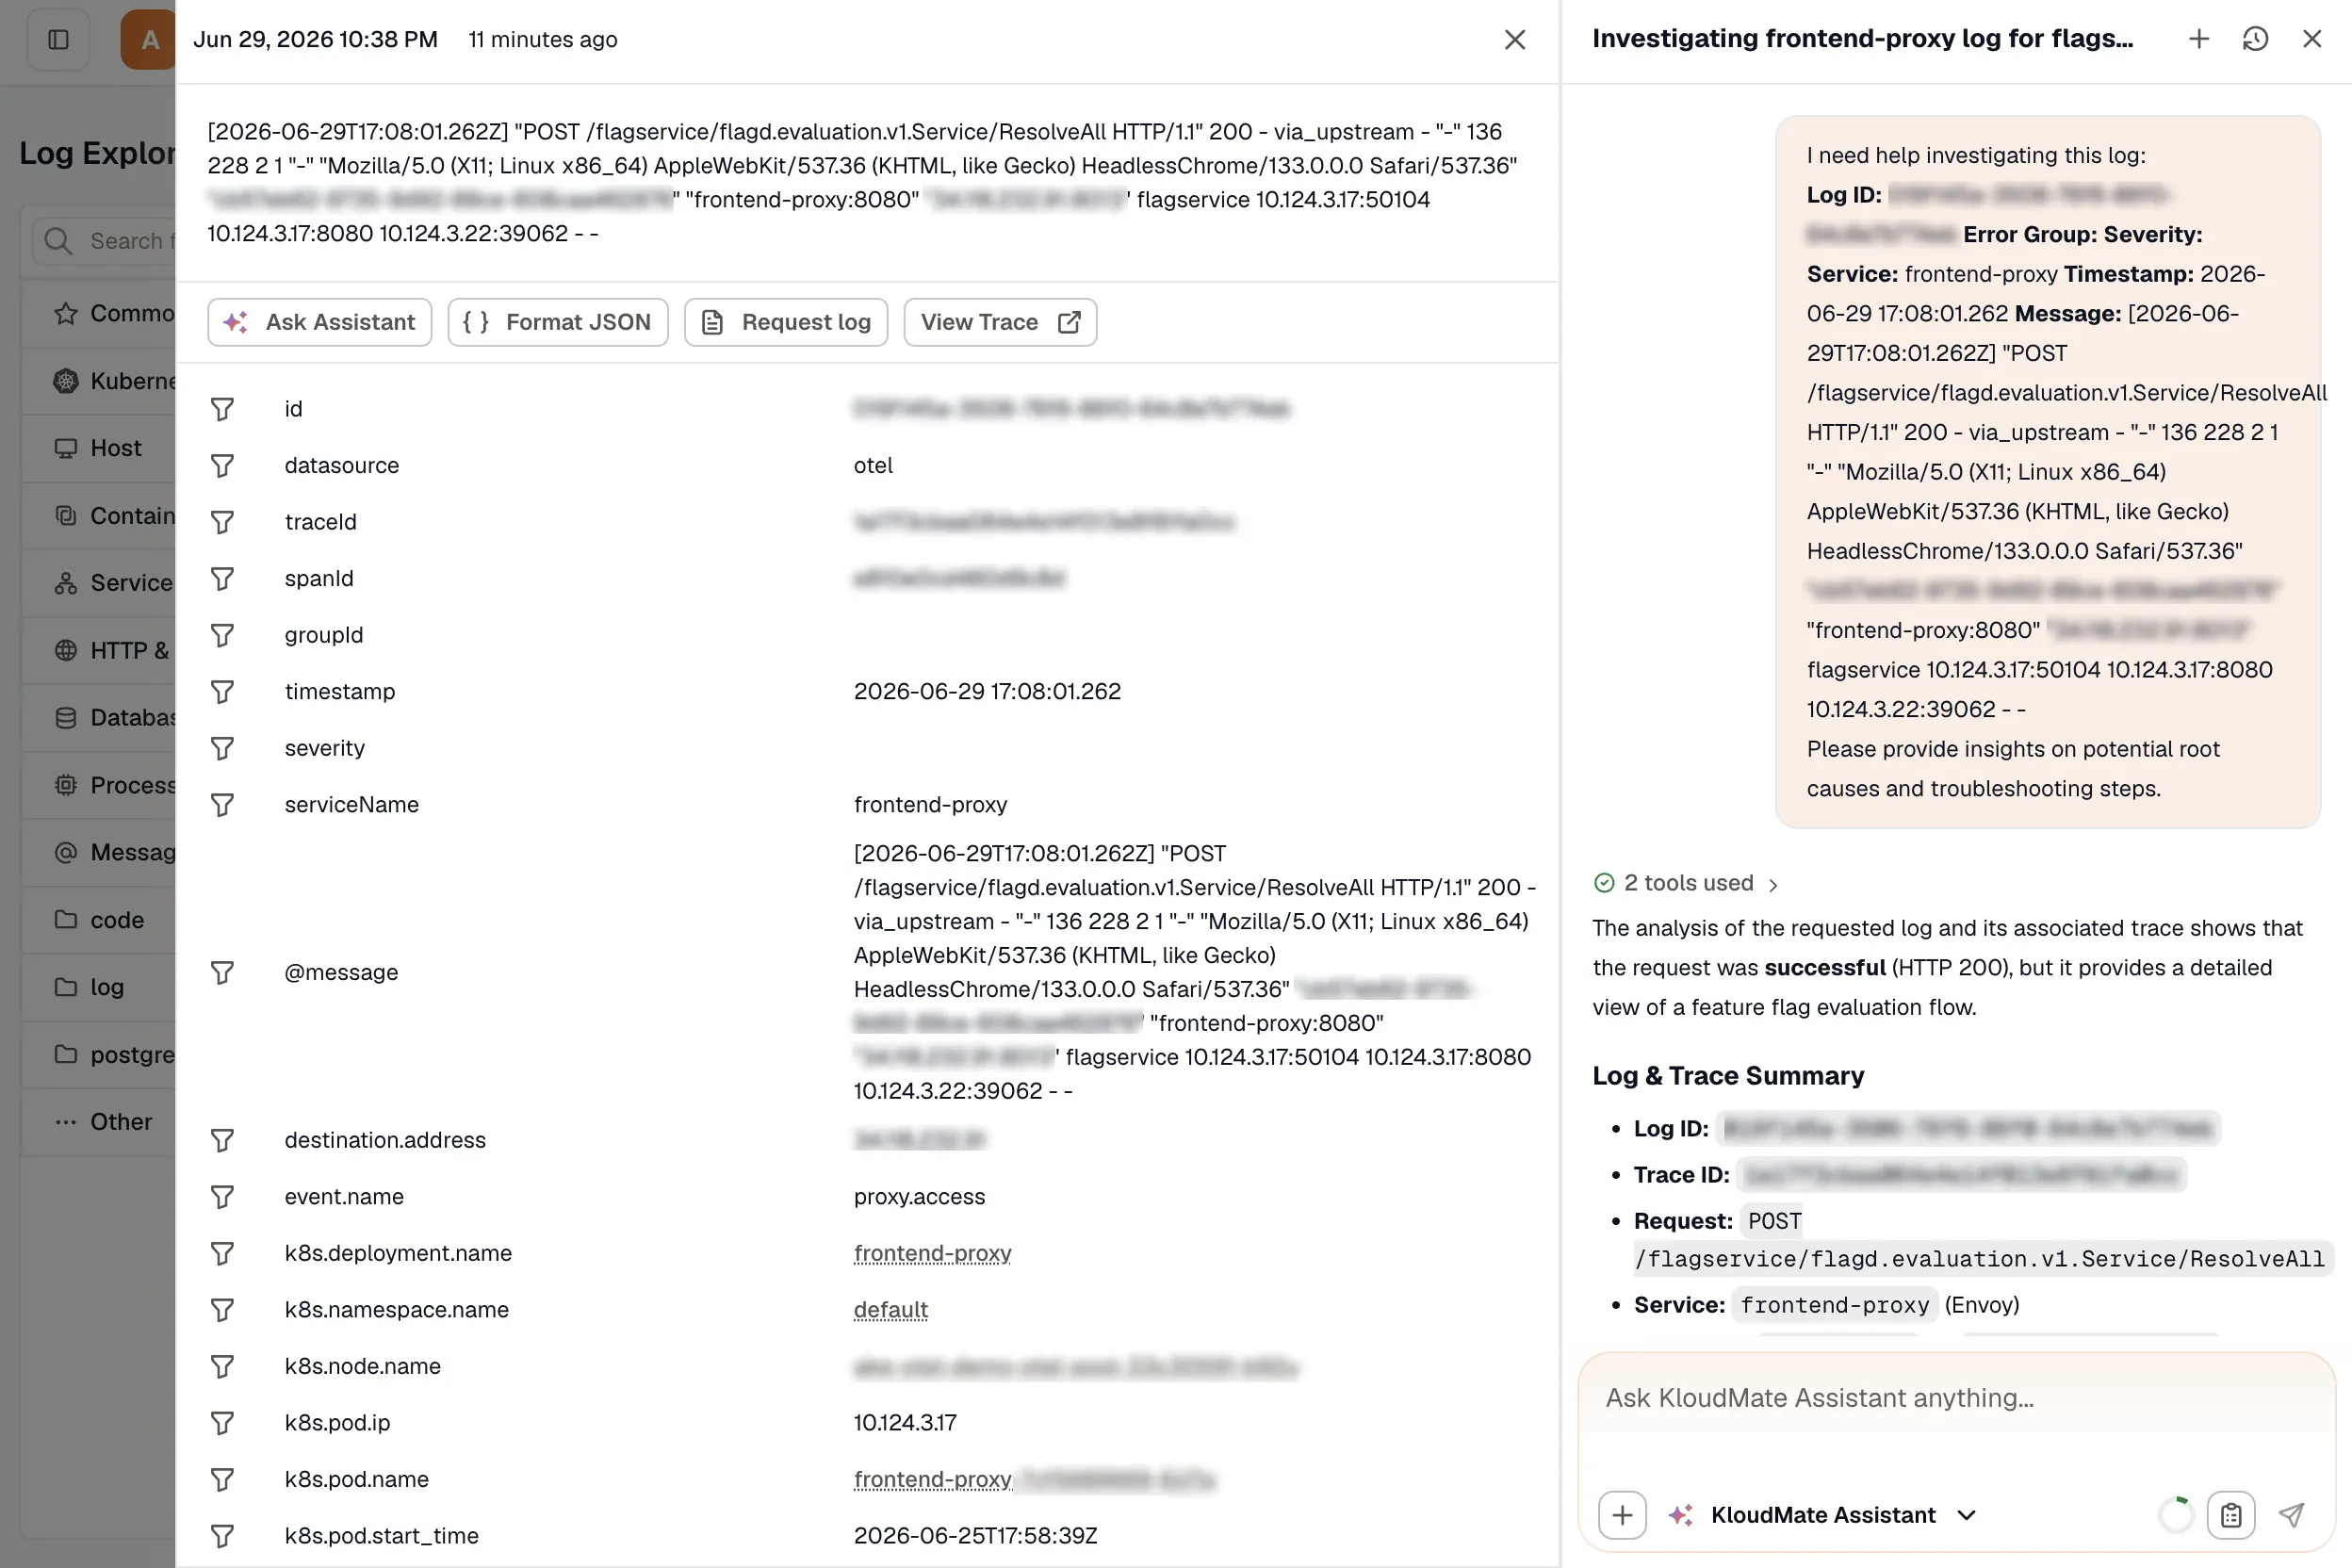
Refer to the KloudMate Assistant documentation for more details.
Stream Logs
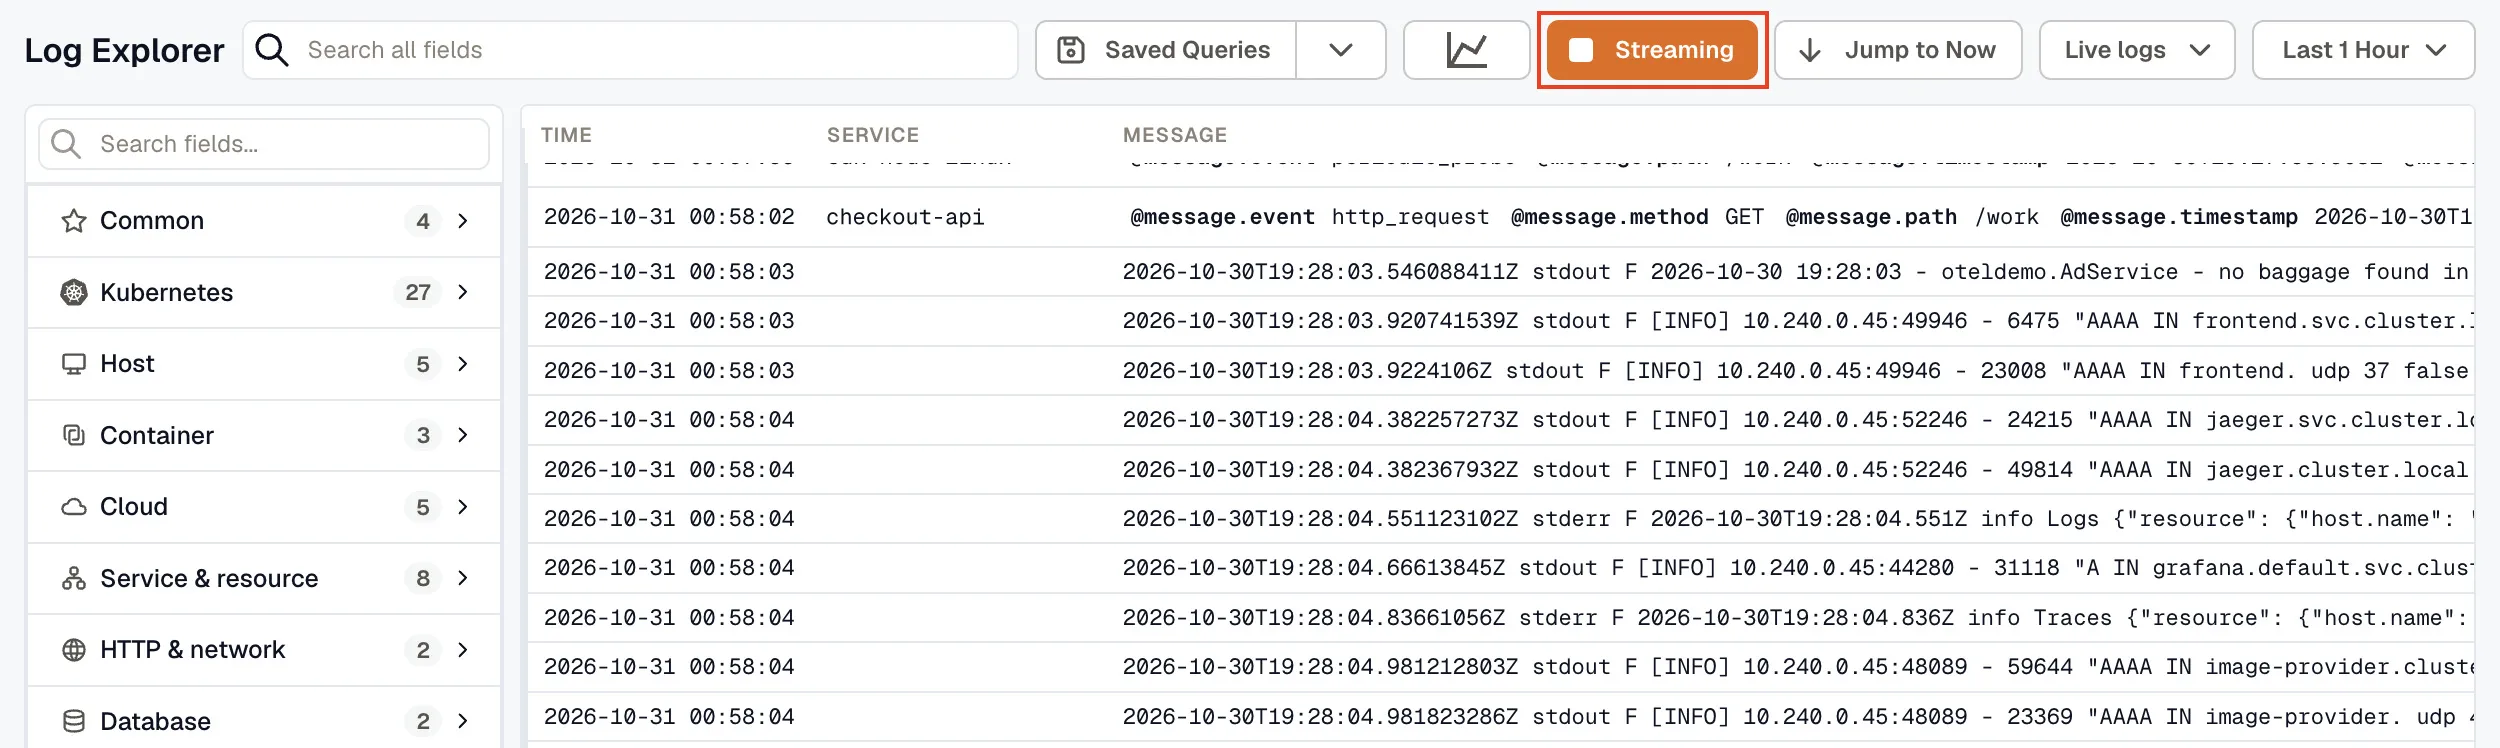
Section titled “Stream Logs”Use Stream to watch logs as they are ingested into KloudMate.
Search Archived Logs
Section titled “Search Archived Logs”If your organization archives logs to S3 with Cold Storage, you can search logs that are older than your log retention. When the selected time range starts before your retention, Log Explorer offers to rehydrate it. To search a rehydration, click Live logs and select it under Rehydrated.
See Rehydrate archived logs for how rehydration works and what it costs.